Platform · Risk
Fix what attackers are likely to exploit first.
Venevor brings in scanner and endpoint findings, enriches them with CISA KEV and EPSS, and ranks them into a fix-first work queue.
- KEV + EPSS
- enrichment
- 4
- finding sources
1Prioritization
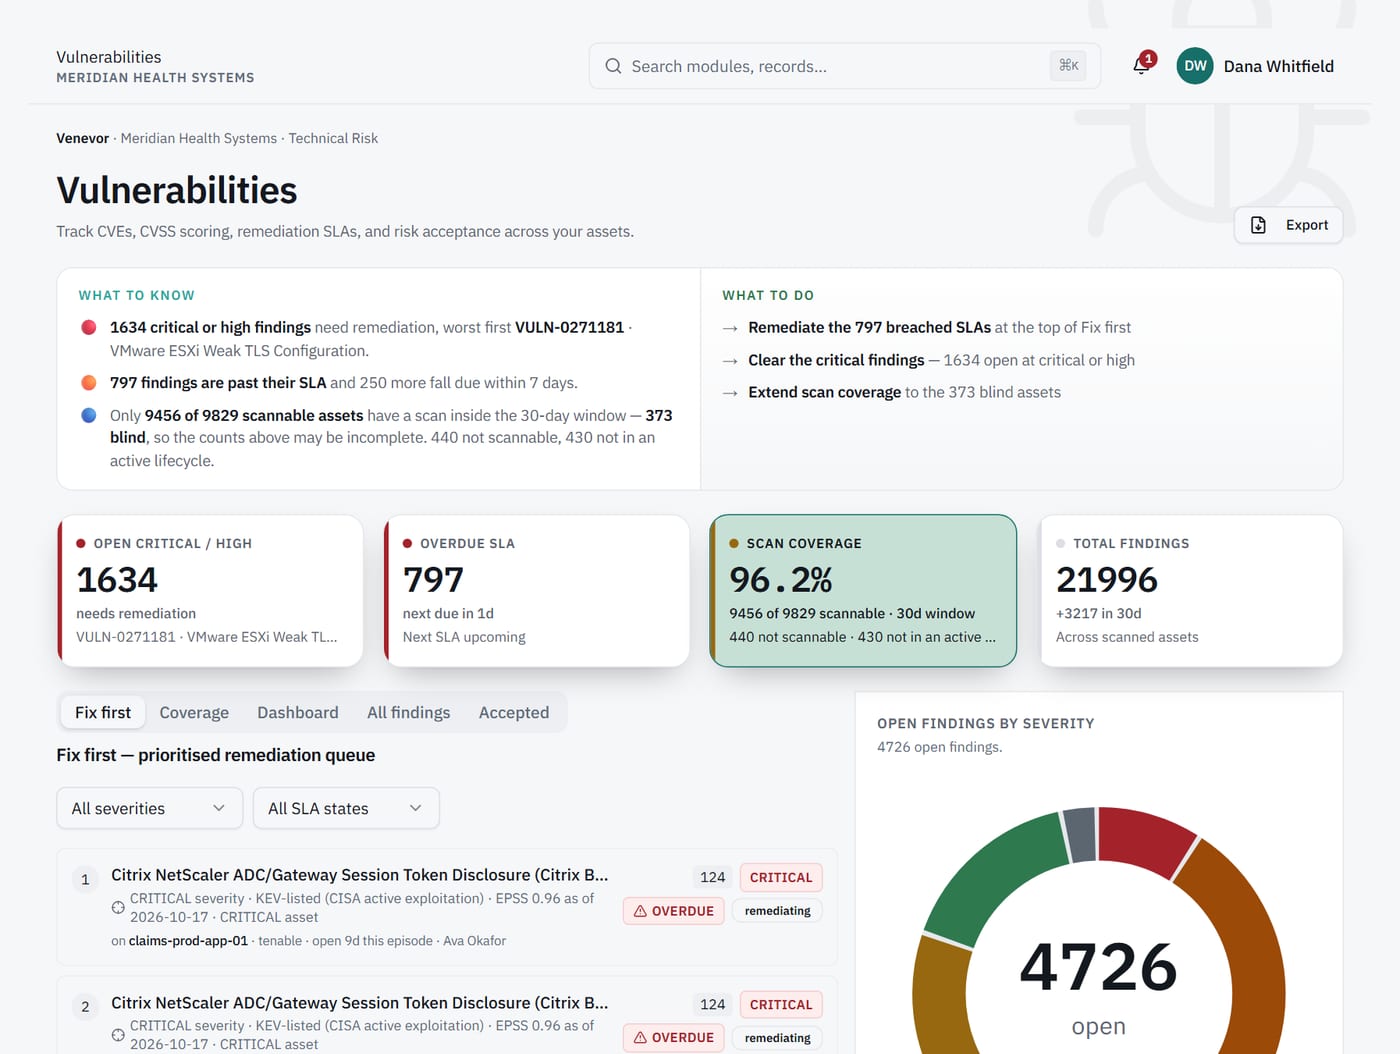
Severity alone does not set the order.
Thousands of high-severity findings cannot all be first. Venevor weights known-exploited vulnerabilities from CISA KEV and likely-exploited ones from EPSS. The result is a fix-first work queue.
2Coverage
Know what your scanners can see.
A clean scan means little if part of the estate was never scanned. Venevor shows scanner coverage and the provenance of each finding. You can see where every finding came from.
3Risk
Connect findings to enterprise risk.
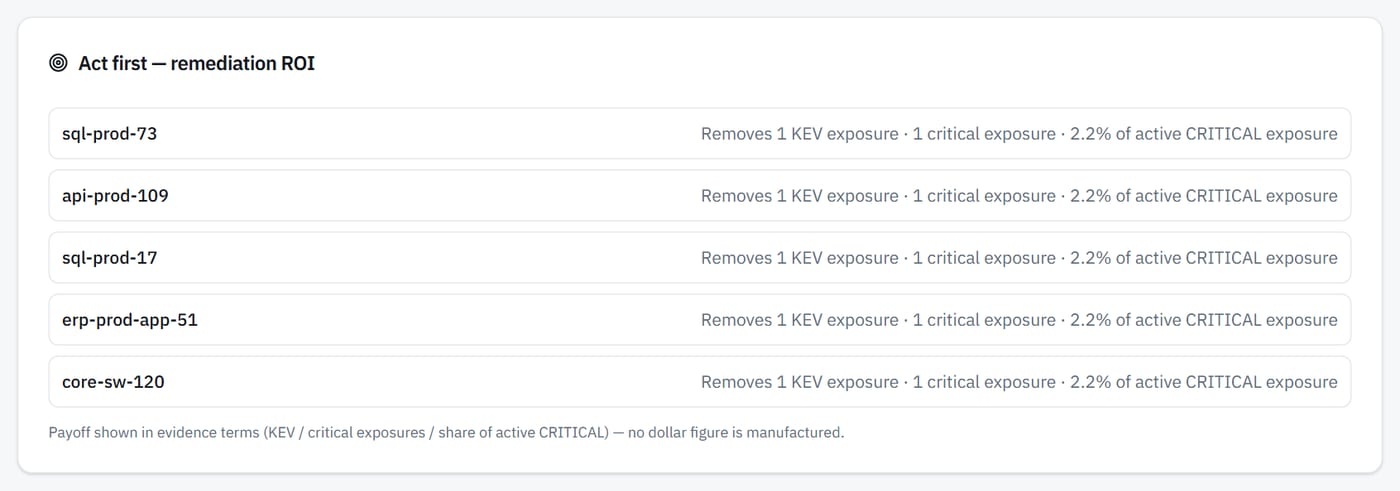
Vulnerability counts rarely reach the risk register. Venevor rolls vulnerabilities up into enterprise technical risk and shows remediation ROI. Fix work connects to what it reduces.
Capabilities
What's included.
Four sources
Findings from Tenable, Qualys, Microsoft Defender and CrowdStrike.
KEV and EPSS
Each finding is enriched with CISA KEV and EPSS data.
Prioritization score
Known-exploited and likely-exploited findings weigh more.
Fix-first queue
One ordered work queue for remediation.
Scanner coverage
See which parts of the estate your scanners reach.
Remediation ROI
See what each fix reduces in technical risk.
Works with
Connected to the rest of Venevor.
FAQ
Common questions.
Which tools does it ingest from?
Tenable, Qualys, Microsoft Defender and CrowdStrike.
How is the order decided?
A prioritization score weights known-exploited vulnerabilities (CISA KEV) and likely-exploited ones (EPSS).
Does it replace our scanner?
No. Venevor reads findings from the scanners and endpoint tools you already run.
Start with the fixes that matter.
Request a demo to see how the fix-first queue is built.