Frameworks · Privacy
HIPAA
Venevor tracks key HIPAA Security Rule standards, checks the safeguards it can read from your systems, and keeps a dated record of the evidence behind each one.
- Issued byU.S. Department of Health and Human Services
- Applies toCovered entities and their business associates
One check
Counts toward
- HIPAAVerified
- NIST CSF 2.0Verified
- SOC 2Verified
- ISO 27001Verified
The framework
What HIPAA asks of you.
What it is
HIPAA is a U.S. federal law, and its Security Rule sets standards for protecting electronic protected health information (ePHI). The rule groups its standards into administrative, physical and technical safeguards, and some implementation specifications are required while others are addressable. The HHS Office for Civil Rights enforces it.
Health Insurance Portability and Accountability Act of 1996
Who needs it
- Hospitals, clinics and health systems
- Health plans and healthcare clearinghouses
- Business associates that handle ePHI for covered entities
1Safeguards
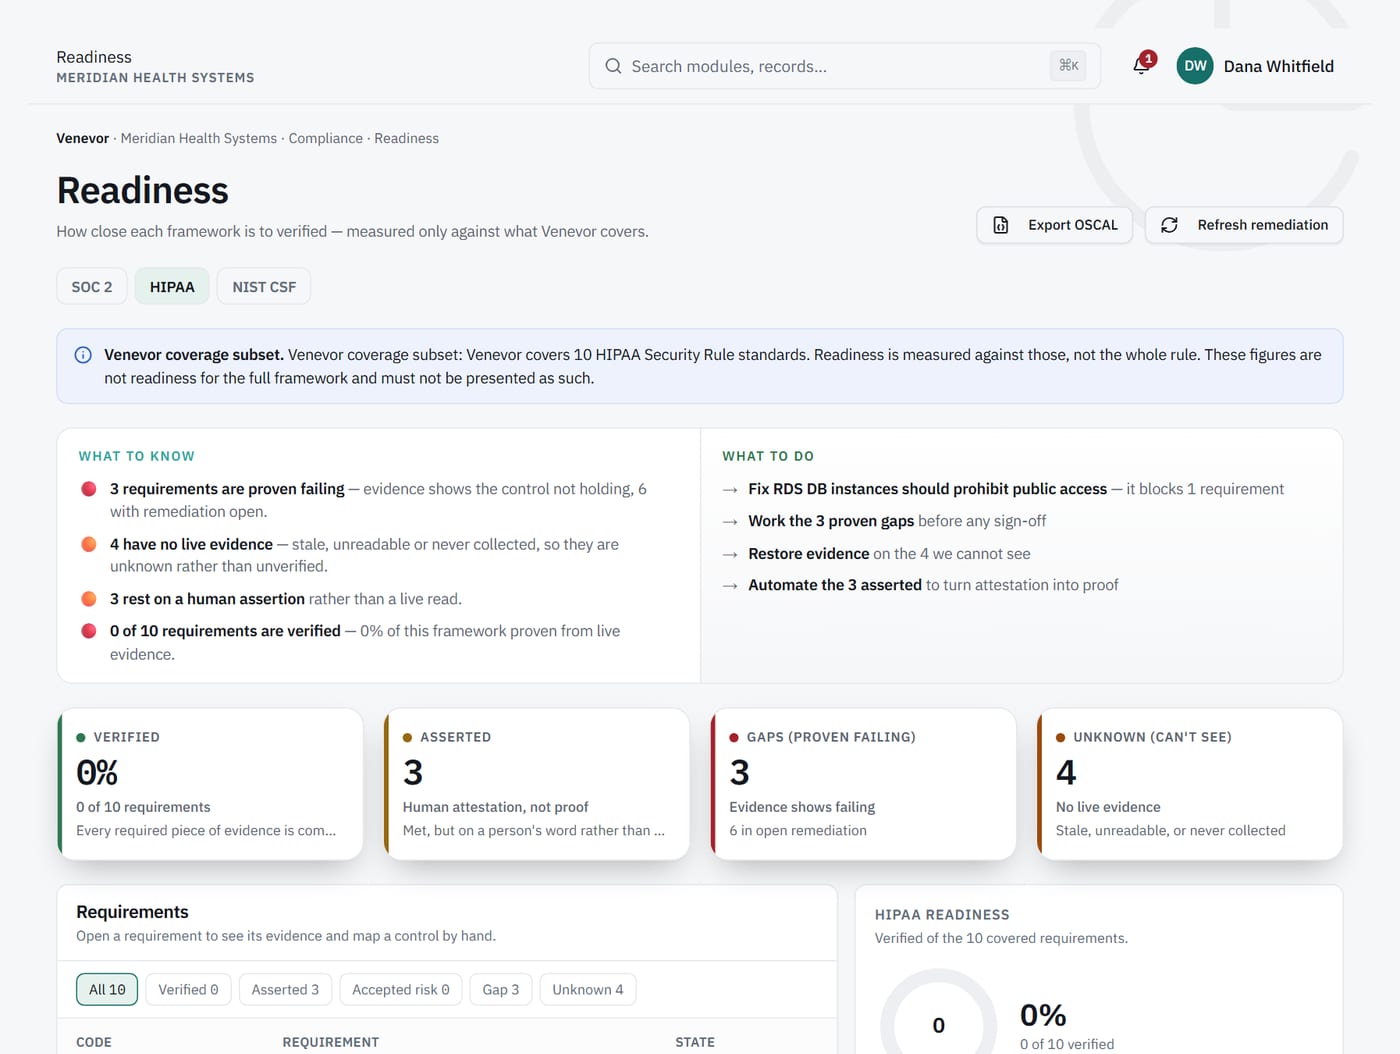
Administrative, physical and technical safeguards in one view
Venevor's HIPAA pack covers key Security Rule standards across all three safeguard groups. Each standard shows its readiness, the controls mapped to it, and the evidence behind them.
2Technical safeguards
Access and audit controls checked against real systems
Connectors to identity, endpoint and cloud systems read the settings behind your technical safeguards. An automated control's status comes only from its latest check.
What it does
Shows when each piece of evidence was collected and whether it is still fresh.
What it never does
Let anyone mark an automated control as compliant by hand.
3Administrative safeguards
Policies your people have approved and read
Security policies go through e-signature approval, and staff acknowledge them. Exceptions carry an owner and an expiry date, so accepted risk stays visible and time-bound.
Capabilities
Built for HIPAA.
Security Rule pack
Administrative, physical and technical safeguard standards, mapped to your controls.
Verified kept separate
Readiness keeps verified and asserted apart and never adds them together.
Evidence freshness
Each piece of evidence is marked fresh, stale or cannot verify.
Incident tracking
Incidents record their breach-notification status alongside the investigation.
Exceptions with expiry
Every exception has an owner and an expiry date, and it never overrides an automated status.
Auditor workspace
Assessors and auditors get access to the evidence, with export.
One set of evidence
The same checks count toward other frameworks.
- Security
NIST CSF 2.0
Map your program to the six CSF 2.0 Functions.
See NIST CSF 2.0 → - Security
SOC 2
Prepare Common Criteria evidence for your SOC 2 audit.
See SOC 2 → - Security
ISO 27001
Prepare your ISMS and Annex A controls for certification.
See ISO 27001 → - Compliance
Compliance automation
Controls that prove themselves from live checks.
Learn more → - Compliance
Policy management
Policies approved, signed, acknowledged and exported.
Learn more → - Risk
Enterprise risk
A risk register scored, treated and tied to controls.
Learn more →
FAQ
HIPAA questions.
Does Venevor make us HIPAA compliant?
No software can do that. Compliance depends on how your organization protects ePHI. Venevor helps you track key Security Rule standards, collect evidence and see where gaps remain.
Does the HIPAA pack cover the Privacy Rule and Breach Notification Rule?
The pack covers key Security Rule standards. Privacy Rule and Breach Notification Rule obligations are outside it, though incidents in Venevor do record a breach-notification status for your own tracking.
Can Venevor help with our security risk analysis?
The Security Rule requires a risk analysis. Venevor's risk register records risks, owners and treatment, and links them to related controls, so the analysis and the evidence sit together.
Can an outside assessor review our evidence?
Yes. Give them a dedicated workspace with the controls, evidence and history in scope. They can export what they need and cannot change anything.
See your HIPAA readiness on real evidence.
A walkthrough built around your frameworks and the systems you already run.