Frameworks · Privacy
EU–US Data Privacy Framework
Venevor tracks your obligations under the DPF Principles, keeps your privacy policies approved and acknowledged, and holds the evidence you need each time you recertify.
- Issued byU.S. Department of Commerce
- Applies toU.S. organizations receiving personal data from the EU
One check
Counts toward
- EU–US Data Privacy FrameworkVerified
- ISO 27001Verified
- SOC 2Verified
The framework
What EU–US Data Privacy Framework asks of you.
What it is
The EU–U.S. Data Privacy Framework lets participating U.S. organizations receive personal data from the European Union under a 2023 adequacy decision by the European Commission. Organizations self-certify through the U.S. Department of Commerce, commit to the DPF Principles, and recertify every year. The Federal Trade Commission or the Department of Transportation enforces those commitments.
EU–U.S. Data Privacy Framework
Who needs it
- U.S. companies that receive personal data from the EU
- SaaS providers serving European customers
- Privacy and legal teams managing annual recertification
1DPF Principles
Each Principle tracked with its evidence
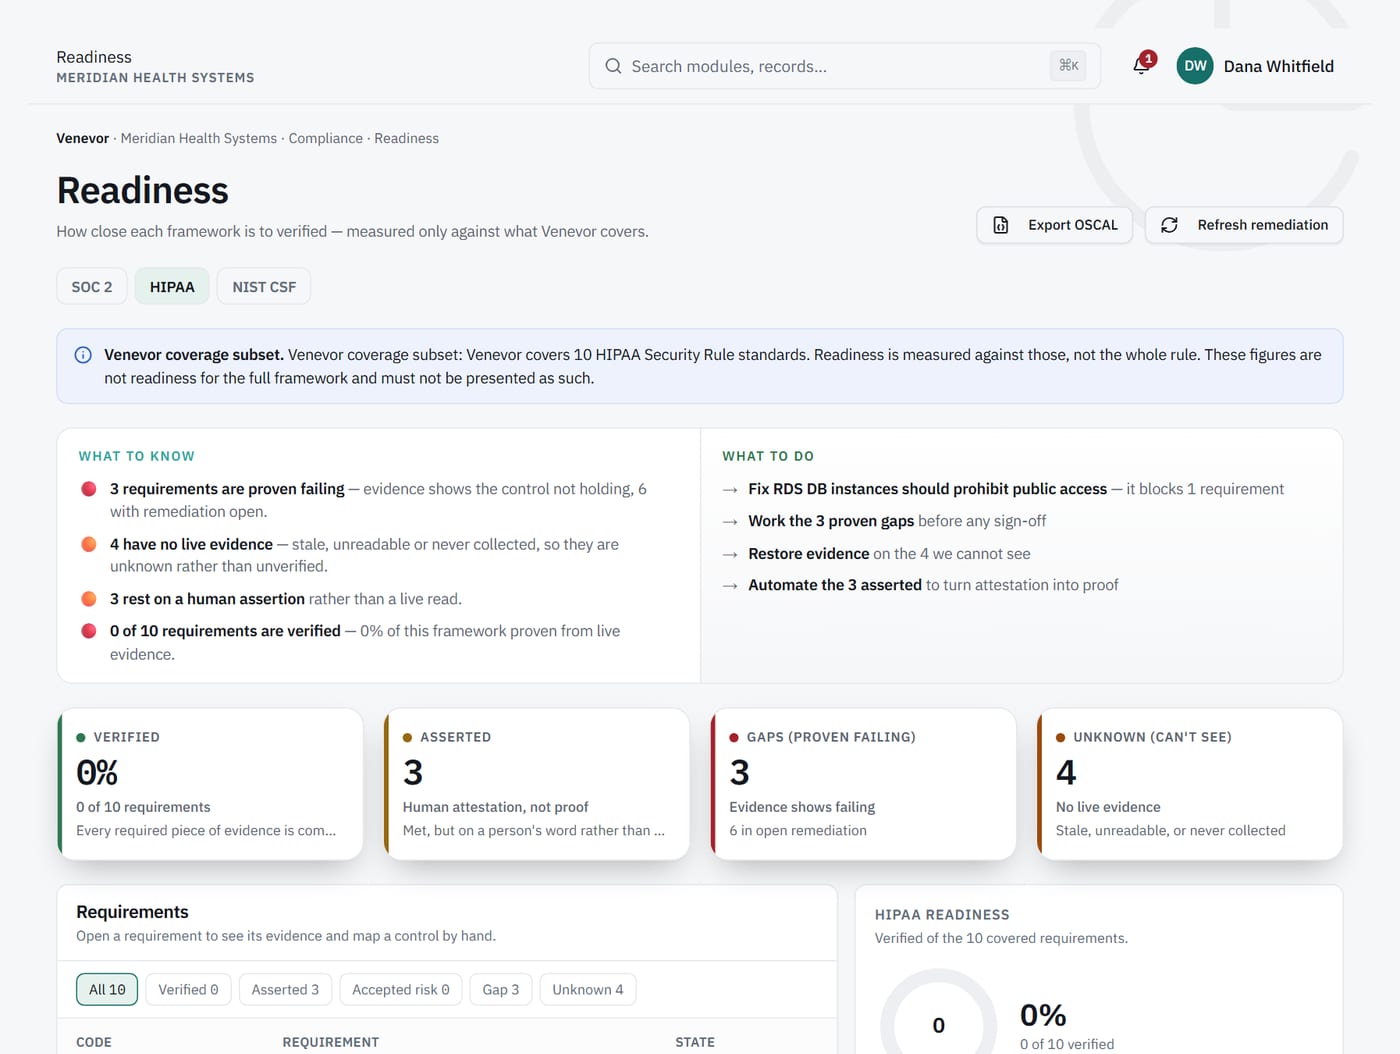
The Principles cover notice, choice, accountability for onward transfer, security, data integrity and purpose limitation, access, and recourse. Venevor maps your controls to them and shows readiness for each.
2Onward transfer
Know which vendors receive the data
Accountability for onward transfer means knowing which third parties get the personal data you received. Vendor questionnaires and third-party records keep that review in one place.
3Recertification
Evidence ready for every annual recertification
Your privacy policy has to match what you certify. Policies go through e-signature approval and acknowledgement, and evidence is timestamped and never edited.
What it does
Keeps a timestamped record of each policy approval.
What it never does
Self-certify on your behalf. That filing stays with your organization.
Capabilities
Built for EU–US Data Privacy Framework.
DPF Principles pack
Each Principle mapped to your controls, with readiness shown for each.
Privacy policy approvals
Policies are approved with e-signature and acknowledged by staff, and the record is kept.
Vendor questionnaires
Review the third parties that receive transferred data and keep their responses.
Incident tracking
Incidents record their breach-notification status alongside the investigation.
Security Principle crosswalk
Controls checked for SOC 2 or ISO 27001 also count toward the Security Principle.
Exceptions with expiry
Every exception has an owner and an expiry date, and it never overrides an automated status.
One set of evidence
The same checks count toward other frameworks.
- Security
ISO 27001
Prepare your ISMS and Annex A controls for certification.
See ISO 27001 → - Security
SOC 2
Prepare Common Criteria evidence for your SOC 2 audit.
See SOC 2 → - Compliance
Policy management
Policies approved, signed, acknowledged and exported.
Learn more → - Operations
Third-party risk
Vendor questionnaires, portal and approval routing.
Learn more → - Compliance
Compliance automation
Controls that prove themselves from live checks.
Learn more →
FAQ
EU–US Data Privacy Framework questions.
Does Venevor self-certify us to the DPF?
No. Your organization self-certifies with the U.S. Department of Commerce. Venevor helps you track the Principles and keep the evidence behind your certification.
Is the DPF a replacement for GDPR compliance?
No. The DPF is a mechanism for transferring personal data from the EU to the U.S. It does not cover your other GDPR obligations, and Venevor's DPF pack tracks the DPF Principles only.
How does the Security Principle relate to SOC 2 or ISO 27001?
Many of the same controls apply. One check maps to every framework it supports, so evidence collected for SOC 2 or ISO 27001 also counts here.
What about data from the UK or Switzerland?
The UK Extension and the Swiss–U.S. Data Privacy Framework are separate programs that organizations join alongside the EU–U.S. framework. Venevor's pack is built around the EU–U.S. DPF.
See your EU–US Data Privacy Framework readiness on real evidence.
A walkthrough built around your frameworks and the systems you already run.